

Sign-in and registration
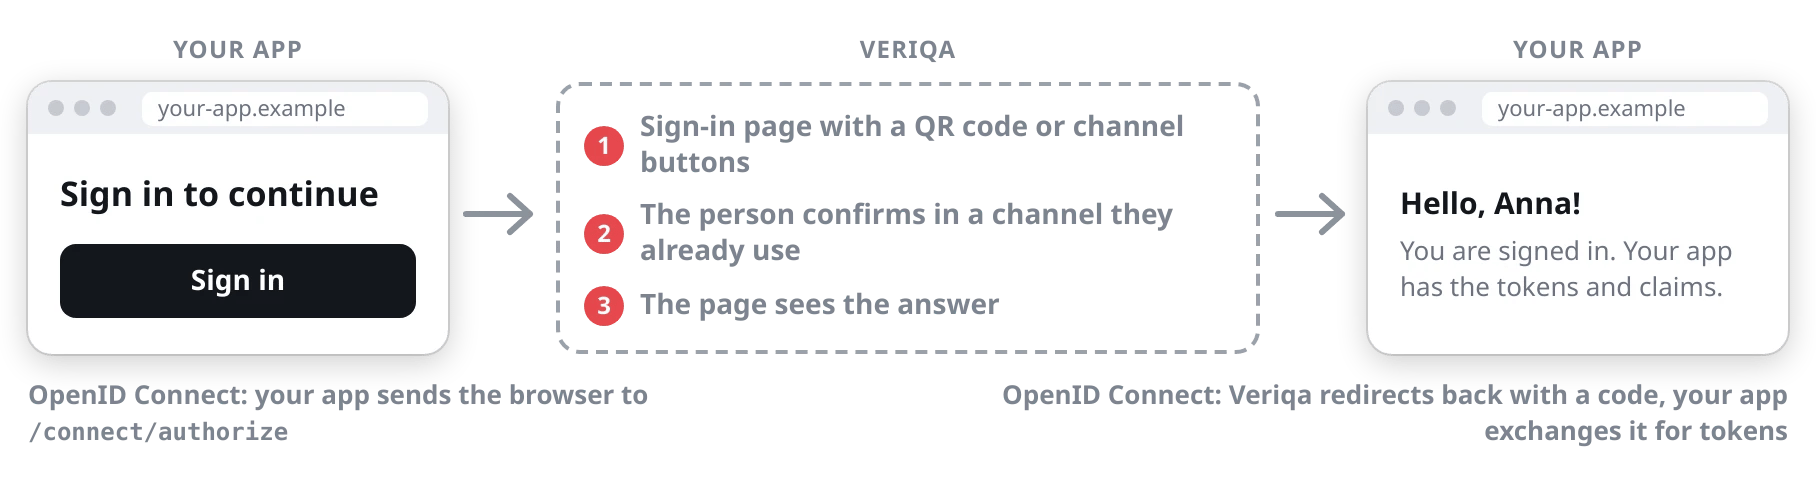
/connect/authorize, the
sign-in window shows a QR code (or a channel button on the phone), the user confirms in the
messaging app, and your application exchanges the code for tokens at /connect/token.
- Registration happens in the same step — there is no form and no password to create.
- The result is an
id_tokenwithsub,auth_timeand the claims you asked for; the session is yours to open. - Your application stays a plain OIDC client: no Veriqa package, no SDK, only configuration.
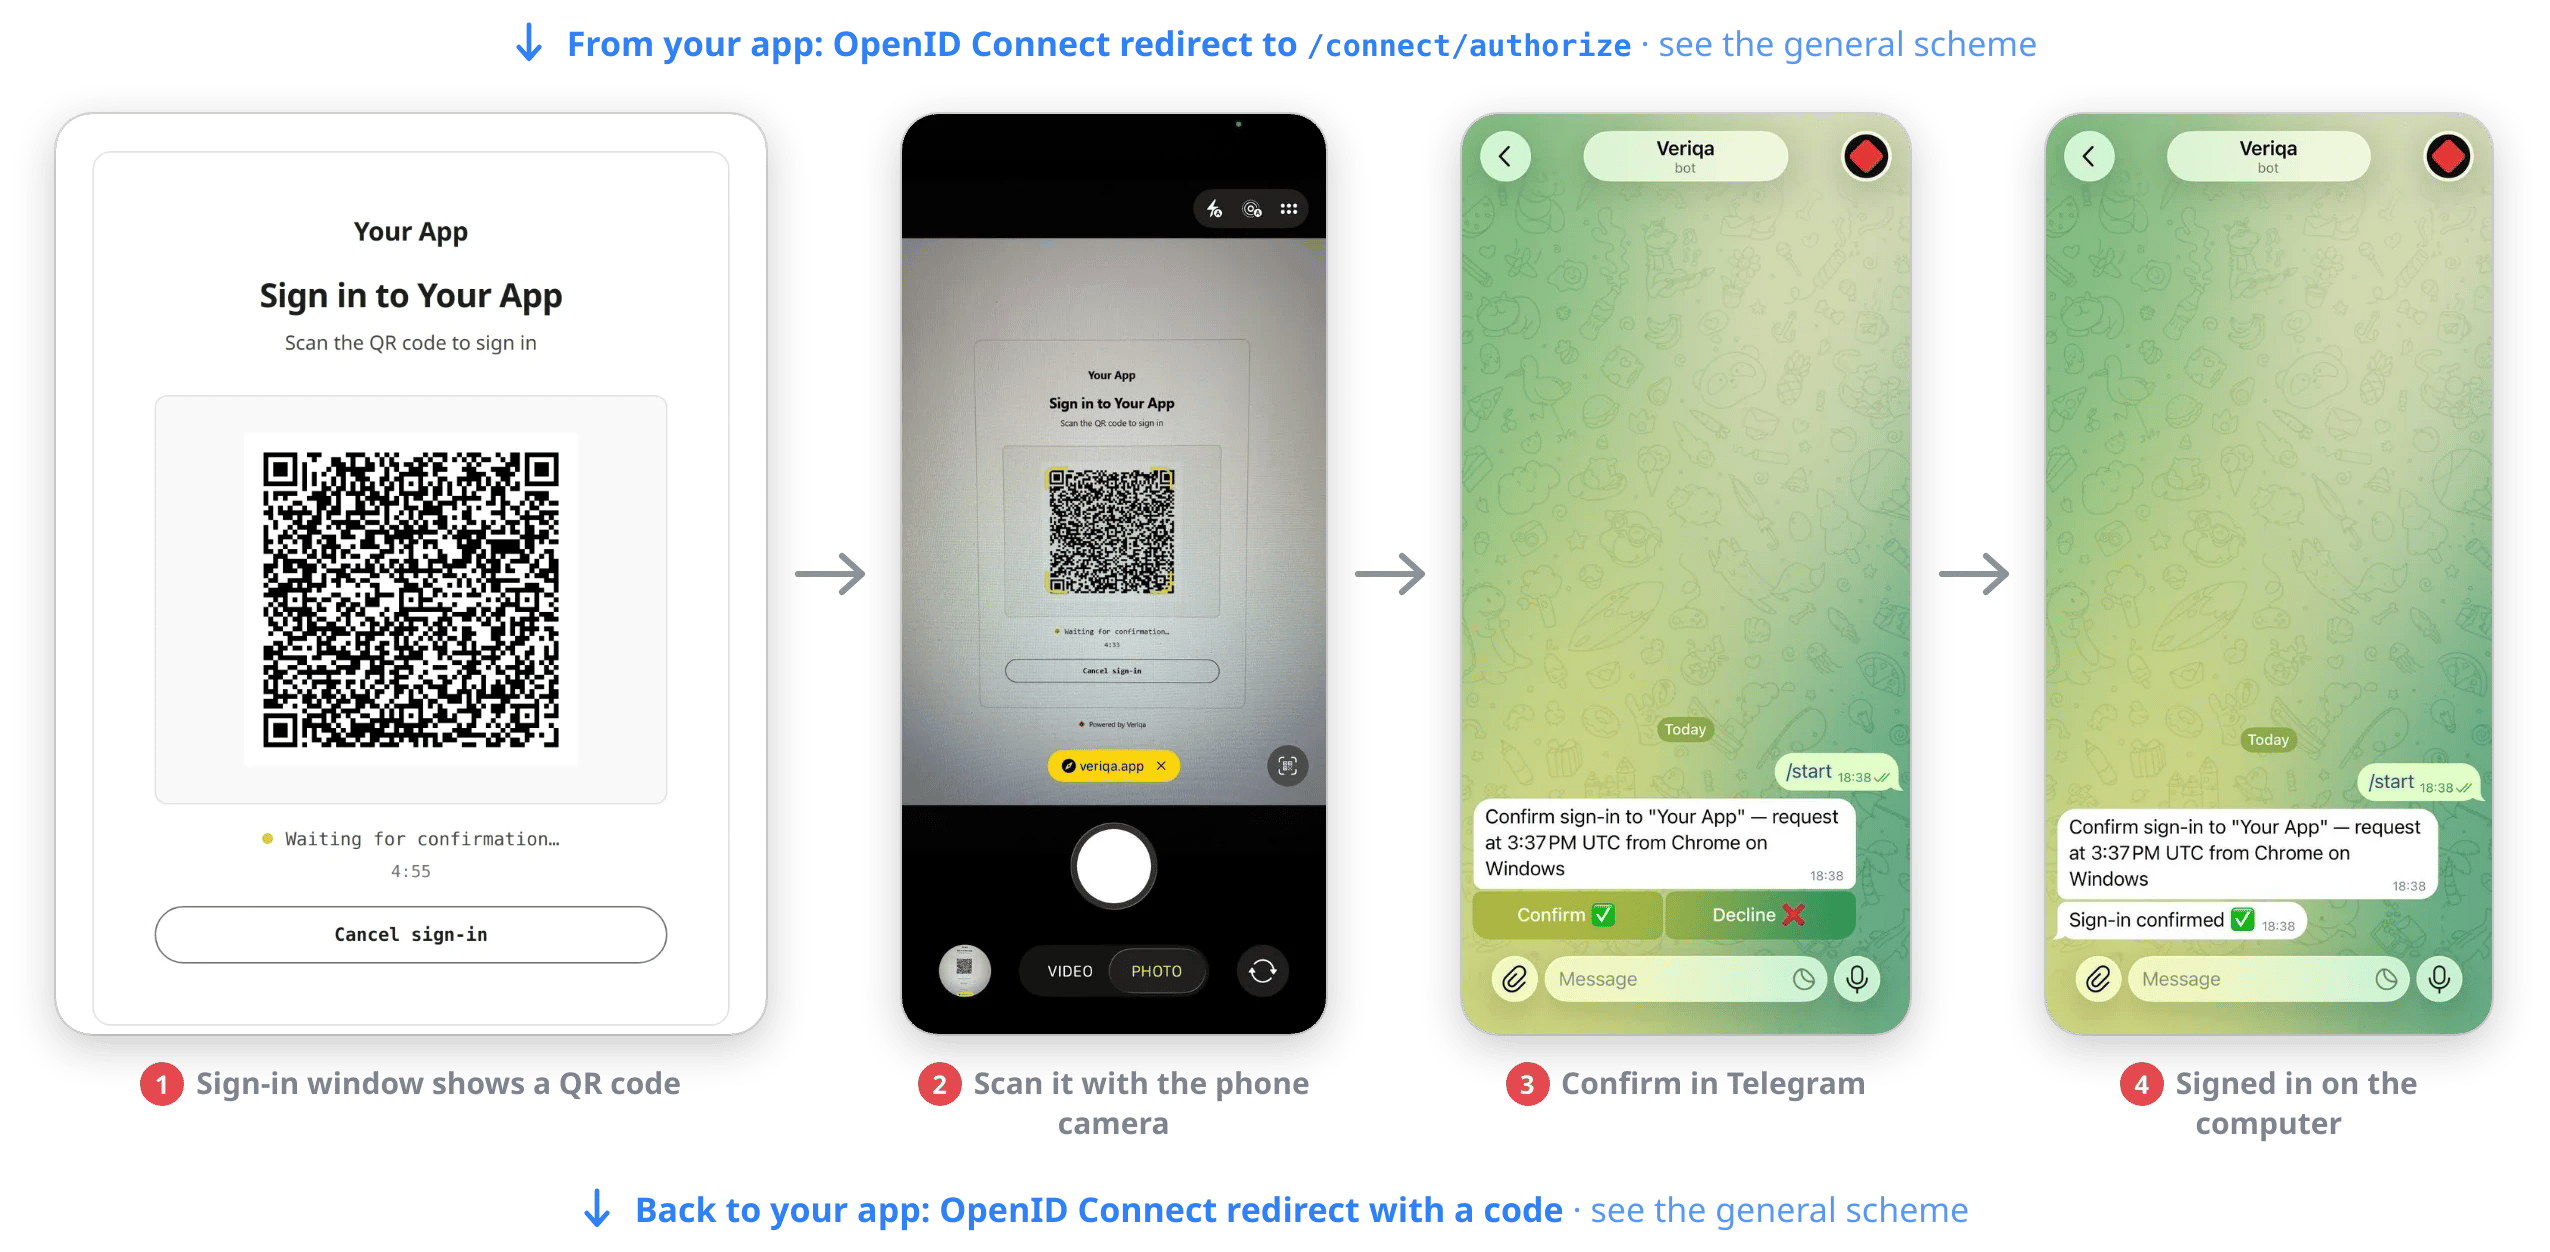
A sign-in: a QR code, the phone camera, one tap in the messaging app.
Server-to-server transaction
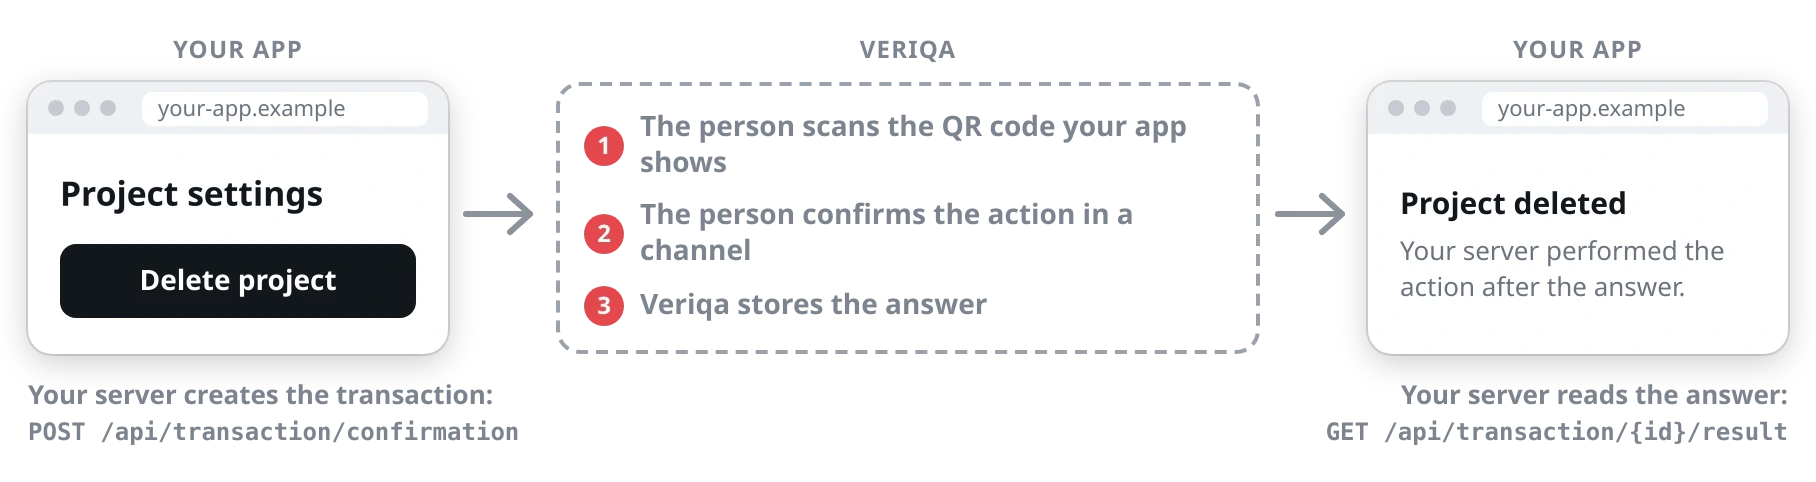
POST /api/transaction/confirmation for a declared action type, shows the user the QR code or
link from the response, and reads the outcome with GET /api/transaction/{id}/result.
- The user sees wording declared on your host with typed slot values — “Delete ticket A-900?”, “Buy for 4.99 EUR?” — never free text from the caller.
expected_identitieslets only a specific person confirm — for example the owner of the current session.- No session is created. A confirmed transaction can optionally be exchanged for the
id_tokenof the person who confirmed.
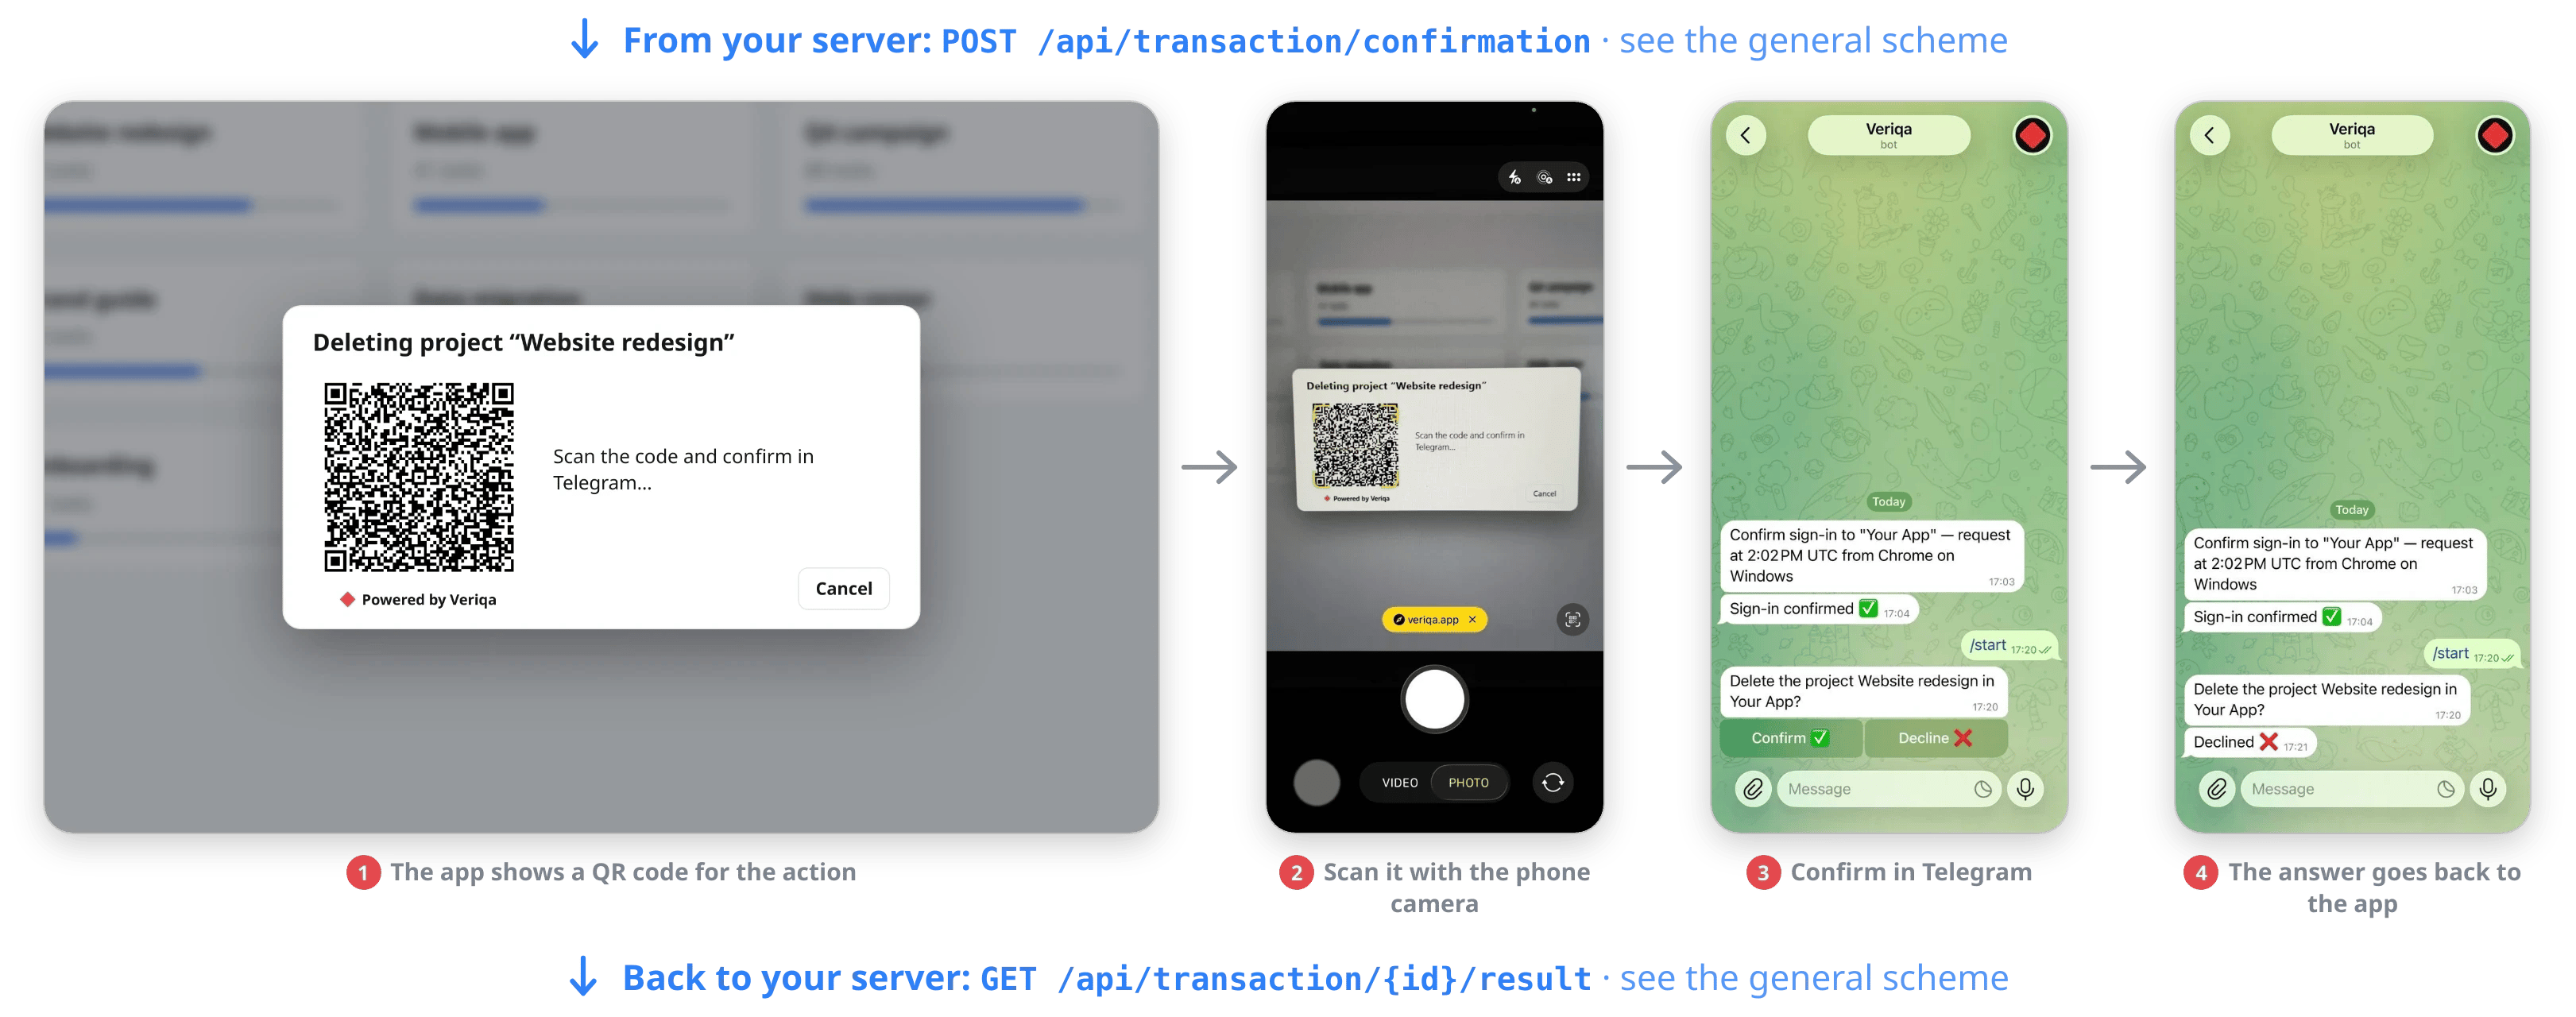
A server-to-server transaction: the app shows a QR code, and the user scans it with their phone camera and declines the request in Telegram. The app receives the answer.
How they differ
Scenarios and their mechanism
Every use case is listed on All use cases.